Mastering the Connection with a Controller Network Access Guide
Mastering the Connection with a Controller Network Access Guide
What Controller Network Access Really Means (And Why It Matters)

Controller network access is the practice of using centralized systems to manage, secure, and automate who and what connects to your network — whether that’s a virtual server in a data center, an employee’s laptop, or the front door of your building.
Here’s a quick breakdown of the main types:
| Type | What It Controls | Common Use Case |
|---|---|---|
| SDN Controller | Virtual network infrastructure | Data center automation |
| NAC System | User and device access | BYOD, IoT, guest access |
| Physical Door Controller | Building entry points | Office or facility security |
| Wi-Fi Access Controller | Wireless network connections | Guest and employee Wi-Fi |
As endpoints multiply — from personal devices to smart building sensors — managing who gets in (and who doesn’t) becomes critical. A single unmonitored device can open the door to a serious breach.
This is no longer just an IT problem. Homeowners and small business owners are running networks that rival small enterprises. You may have security cameras, smart locks, automation hubs, and employee devices all sharing the same connection. Without proper controller network access, every one of those devices is a potential vulnerability.
The good news: modern solutions make centralized, secure network control more accessible than ever.
Understanding Controller Network Access and Its Core Types
When we talk about controller network access, we are describing the “brain” of a modern digital environment. In the past, if you wanted to change a security rule or grant someone access to a specific room, you had to manually configure individual devices. Today, we use controllers to handle everything from a single, programmable interface.
To truly master your connection, you need to understand the different flavors of controllers available. For those looking to dive deep into modern security philosophy, Zero Trust Access for Dummies provides an excellent foundation on the “never trust, always verify” mindset that drives these technologies.
Defining Controller Network Access in Modern Infrastructure
At its heart, controller network access is about centralized management. Instead of hopping from one switch to another or visiting every door in a building, we use a controller to push policies across the entire infrastructure. This allows for:
- Programmable Automation: Automatically adjusting network paths or security rules based on real-time needs.
- Policy Enforcement: Ensuring that every device, whether it’s a smart thermostat in Troy or a server in a West Bloomfield data center, follows the same security protocols.
- Network Visibility: Seeing exactly who is on the network and what they are doing at any given moment.
The Role of Hardware vs. Software Controllers
In our work across Michigan, from the bustling offices of Southfield to residential estates in Bloomfield Hills, we see a mix of hardware and software solutions.
- Software Controllers (Virtual Appliances): These often run as Virtual Machines (VMs) and are common in Software-Defined Networking (SDN). They are incredibly flexible and can scale up as your needs grow.
- Physical Gateways: These are dedicated hardware devices often used for high-speed traffic or specific security tasks.
- Edge Computing: Some controllers, like those used for door access, live “at the edge.” This means they can still make decisions (like letting you in your house) even if the main internet connection goes down.
- Cloud-Based Management: This allows us to manage networks in Clarkston or Royal Oak from anywhere in the world, providing a “single pane of glass” view.
Software-Defined Networking (SDN) Controllers: Automating Virtual Infrastructure
If you are running a business with virtual servers, an SDN Network Controller is your best friend. It acts as a centralized, programmable point of automation to manage and troubleshoot your virtual network infrastructure. For those technical enthusiasts ready to get their hands dirty, you can learn how to Deploy Network Controller using Windows PowerShell to start automating your environment.
At SmartMait, we specialize in making these complex systems work for you. Whether you need to secure a local office or a large facility, our commercial security services ensure your virtual and physical assets are protected.
Managing Virtual Services via Controller Network Access
An SDN controller doesn’t just “watch” the network; it actively manages services that used to require expensive, standalone hardware.
- Distributed Firewalls: Instead of one big firewall at the edge, the controller “plumbs” firewall rules directly into the virtual switch ports. These rules move with your workloads—if you move a VM from one host to another, the security follows it.
- Software Load Balancers (SLB): These distribute traffic evenly across your servers to ensure high performance and prevent crashes.
- RAS Gateways: Essential for site-to-site VPN connectivity, allowing remote offices in Farmington Hills to connect securely to a central hub in Detroit.
- Virtual Appliance Chaining: This allows you to “string together” different services, like a firewall followed by an intrusion detection system, all within the virtual space.
API Communication Paths: Northbound and Southbound
The magic of the SDN controller lies in its two primary communication paths:
- Northbound API: This is how the controller talks to you (or your management software). It uses a REST API, which allows tools like Windows Admin Center or custom PowerShell scripts to tell the network what to do.
- Southbound API: This is how the controller talks to the network devices. Using protocols like OVSDB (Open vSwitch Database Management Protocol) or WinRM, the controller tells the switches and gateways how to handle traffic.
Network Access Control (NAC): Securing the Corporate Perimeter
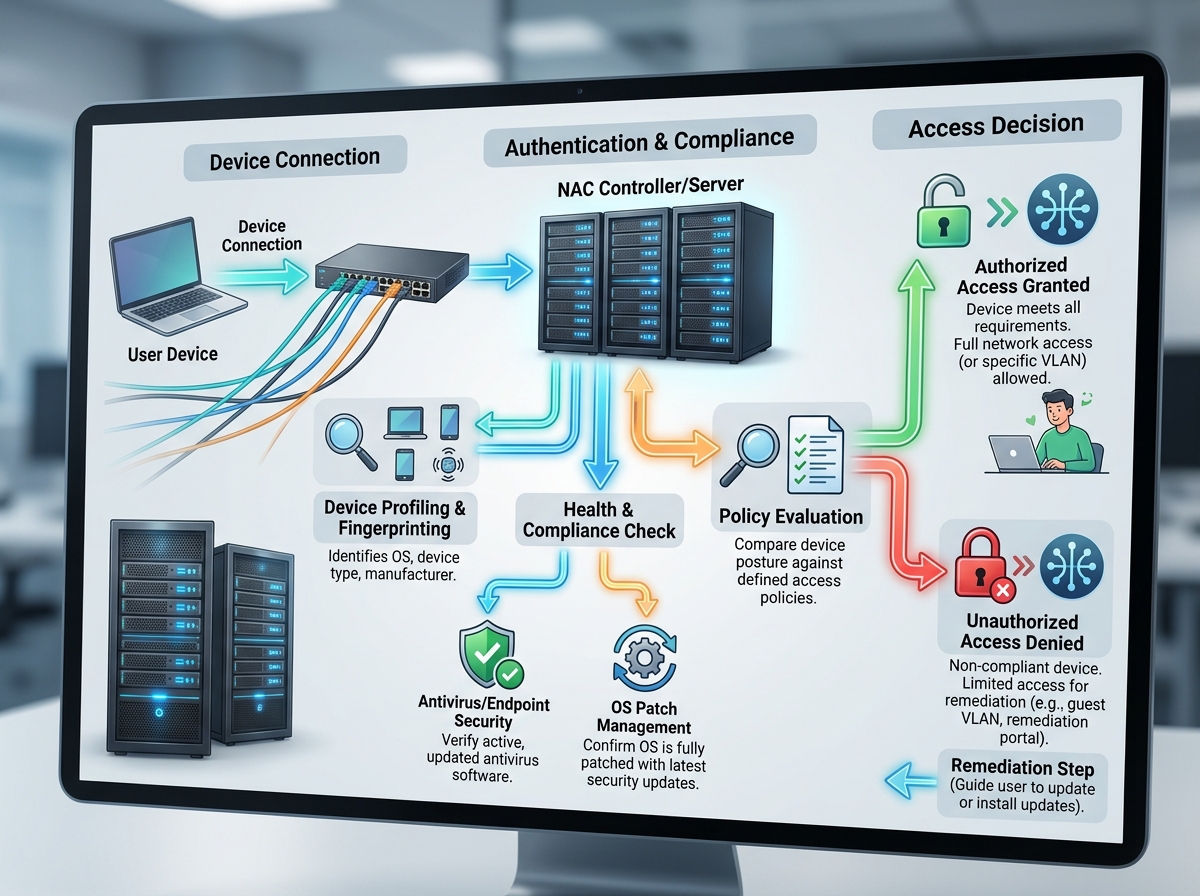
While SDN manages the “pipes,” Network Access Control (NAC) manages the “people and devices.” NAC is the process of restricting unauthorized users and devices from gaining access to your private network. This is particularly vital in the age of mobile work. Research on Mobile Network Access control: Extending Corporate Security Policies to Mobile Devices highlights how crucial it is to extend security beyond the physical office.
Key Capabilities of NAC Solutions
A robust NAC solution doesn’t just ask for a password; it performs a full “health check” on every device.
- Profiling and Visibility: The system identifies what the device is (a laptop, an iPhone, or a smart camera) before it even connects.
- Security Posture Checks: Is the antivirus up to date? Is the OS patched? If not, the NAC can deny access.
- Incident Response: If a device starts acting strangely (like trying to access files it shouldn’t), the NAC can automatically isolate it.
- Guest Networking: Providing temporary, restricted access for visitors in your Troy office without giving them the keys to the kingdom.
For our residential clients in areas like Bloomfield Township or Rochester Hills, these same principles apply to keeping your home network safe. Check out our residential security options to see how we bring enterprise-grade protection to your front door.
Common Use Cases: BYOD and IoT Security
- BYOD (Bring Your Own Device): Employees love using their own phones. NAC ensures those personal devices don’t bring malware into your business.
- IoT (Internet of Things): Smart devices are notorious for poor security. NAC can place your security cameras and smart sensors on a separate, “quarantined” VLAN so they can’t see your private data.
- Automated Remediation: If a device is out of compliance, the NAC can redirect it to a “remediation” portal where the user can download the necessary updates before being allowed back on the main network.
Physical and Wireless Controller Network Access Solutions
Security isn’t just digital. Controller network access also extends to the physical world through network door controllers and advanced Wi-Fi management.
Securing Physical Spaces with Network Door Controllers
Gone are the days of simple metal keys. Modern network door controllers, like the Axis A18, offer complete control for up to eight doors.
- Scalability: You can start with one door in a Clarkston storefront and grow to hundreds of doors across multiple sites in Macomb County.
- PoE Power: Power over Ethernet means you only need one cable to provide both data and power to the controller, locks, and readers.
- Bidirectional Communication: Using the OSDP (Open Supervised Device Protocol) standard ensures that the communication between the reader and the controller is encrypted and secure.
- Edge Security: With hardware-based cybersecurity (like EAL6+ certified modules), these controllers are hardened against hacking attempts.
Optimizing Wireless Controller Network Access
Wi-Fi is no longer a luxury; it’s a utility. Whether you’re running a boutique in Birmingham or a large public venue in Detroit, managing your wireless controller network access is key to a good user experience.
- Cloud-Operated Wi-Fi: Manage multiple locations from one dashboard.
- Captive Portals: Use custom login pages for guests, which can be used for marketing or even monetization.
- Seamless Roaming: Ensure users don’t drop their connection as they move from the lobby to the conference room.
Deployment and Security Best Practices for Network Controllers
Setting up a controller isn’t just a “plug and play” affair. To ensure reliability and security, there are several critical standards to follow.
Critical Deployment Considerations
If you’re deploying a Network Controller for SDN, remember the “Rule of Three.”
- High Availability: A Network Controller requires a minimum of three VMs to provide high availability. If one VM fails, the others keep the network running.
- Dedicated VMs: Never deploy the Network Controller on the physical hosts themselves; always use dedicated virtual machines.
- Physical Topology: Ensure your management network is physically or logically separated from your workload traffic to prevent “bottlenecks” or security leaks.
- Configuration Monitoring: The controller should automatically remediate “configuration drift,” meaning if a setting is changed accidentally, the controller switches it back to the authorized state.
Essential Security Measures for Controllers
Securing the controller itself is just as important as the network it manages.
- Authentication Modes: Use Kerberos for domain-joined environments or X509 certificates for non-domain setups. Avoid using “None” for authentication in any production environment!
- Encryption: All communication paths (Northbound, Southbound, and Cluster) should be encrypted using SSL or WCF Transport encryption.
- Lateral Threat Prevention: Use default network policies that block all inbound access to virtual machines by default. This prevents a threat from spreading “sideways” through your network if one machine is compromised.
For those interested in the cutting edge of this field, there is fascinating scientific research on Flow-based Network Access Control that explores how SDN can make NAC even more granular and responsive.
Frequently Asked Questions about Controller Network Access
What is the difference between an SDN controller and NAC?
Think of an SDN controller as the “architect” of the network infrastructure—it builds the virtual roads, tunnels, and bridges. NAC is the “security guard” at the gate—it checks the ID and health of every person and vehicle trying to use those roads.
How many VMs are required for a highly available network controller?
For a production environment, you need at least three virtual machines. This ensures that the Service Fabric (the underlying technology that keeps the controller running) can maintain a “quorum” and stay operational even if one node goes offline.
Can controller network access manage both physical and virtual security?
Yes! Modern systems allow us to integrate physical door controllers with video management software. For example, if a door in your Livonia office is propped open, the network controller can automatically trigger a nearby security camera to start recording and send an alert to your phone.
Conclusion
Mastering controller network access is the key to a secure, efficient, and future-proof digital environment. Whether you are protecting a family home in Bloomfield Hills or a multi-site business in Oakland County, the principles remain the same: centralize your management, automate your security, and never stop monitoring.
At SmartMait, we live and breathe this technology. We specialize in seamless smart device integration, using the Z-Wave protocol to ensure all your devices—from your mood lighting to your high-end audio/visual systems—work together in one secure ecosystem. We take the complexity of SDN, NAC, and physical access control and turn it into a simple, user-friendly experience for our Michigan neighbors.
Ready to take control of your network? Master your network with SmartMait commercial solutions and discover how we can help you build a smarter, safer connection today.